Offensive Security for SaaS & MVPs
Close the gaps
before someone exploits them
Penetration testing for SaaS, web apps, and MVPs. I find authorization flaws, business logic gaps, and access control holes — a data leak triggers a GDPR fine, which sends investors running.
Broken Access Control — #1 OWASP threat
Authentication Bypass in API endpoint
// Testing Scope
Web Application Security
Full-scope black-box testing. Auth, authorization, session management, API security, business logic. One misconfigured permission is all it takes for Customer A to see Customer B's data.
MVP & SaaS Penetration Testing
Launching next week? Fast, focused pentests for early-stage products. One critical vulnerability discovered after launch can destroy user trust overnight.
API Security Testing
REST, GraphQL, WebSocket — every endpoint is a potential target. I find broken object-level authorization, mass assignment, injection, and rate-limit bypasses.
AI-Generated Code Audits
Vibe-coded apps often ship without auth checks and with IDOR holes everywhere. I manually audit AI-built architectures to catch what scanners miss.
LLM Integration Security
Your AI wrapper can leak system prompts, expose training data, or execute unauthorized commands. I test against real prompt-injection and data-exfiltration scenarios.
Infrastructure Resilience Testing
Rate-limit bypasses, race conditions, failover gaps, auto-scaling weaknesses. I stress-test whether your infra holds up under load or targeted abuse — not just under ideal conditions.
Cloud Security Review
Open S3 buckets, overprivileged IAM roles, exposed security groups. I audit your AWS, GCP, or Azure infra for the misconfigurations attackers scan for.
Source Code Review
Manual analysis focused on auth flows, sensitive data paths, and business logic. I find the race conditions and IDORs that every SAST tool overlooks.
No-Code / BaaS Configuration Review
Firebase rules written by a non-technical team are a data breach waiting to happen. I review Supabase, Firebase, and no-code stacks.
// How Engagements Run
Every test starts with understanding your product, users, and critical flows. Then I combine automation with targeted manual testing to find what matters.
Scoping & Threat Model
We define scope, user roles, and where the highest-value attack paths are.
Deep Testing
Advanced scanners + custom automation + focused manual verification of auth, authorization, tenant isolation, and business logic.
Safe Exploitation
Findings validated to prove impact without breaking data, production, or operations.
Report & Retest
Clear report with severity, evidence, attack path, and practical fixes. Retest included.
Typical test: 5–10 business days.
// Sample Report
Sample Report
Every engagement ends with a detailed report — non-technical summary for business stakeholders, technical findings with CVSS scores, step-by-step reproduction, and concrete fixes. No fluff, no filler.
// Case Studies
Real security incidents dissected. How they happened, what went wrong, and what you can learn from them — no jargon, just facts.
MOVEit Transfer — Zero-Day SQL Injection, Mass Data Theft
A zero-day SQL injection in Progress MOVEit Transfer (CVE-2023-34362) was exploited by the Cl0p ransomware group. 2,700+ organizations and 95 million individuals affected.
Read More → RCELog4Shell — The Internet's Biggest RCE
A single JNDI lookup in Log4j 2.x gave attackers unauthenticated RCE on systems worldwide. CVSS 10.0. One of the most critical vulnerabilities ever disclosed.
Read More → Supply ChainSolarWinds — The Supply Chain Attack That Broke Fortune 500
Attackers breached SolarWinds Orion's build system and injected the SUNBURST backdoor into official software updates. 18,000 organizations downloaded the malicious update.
Read More →// About
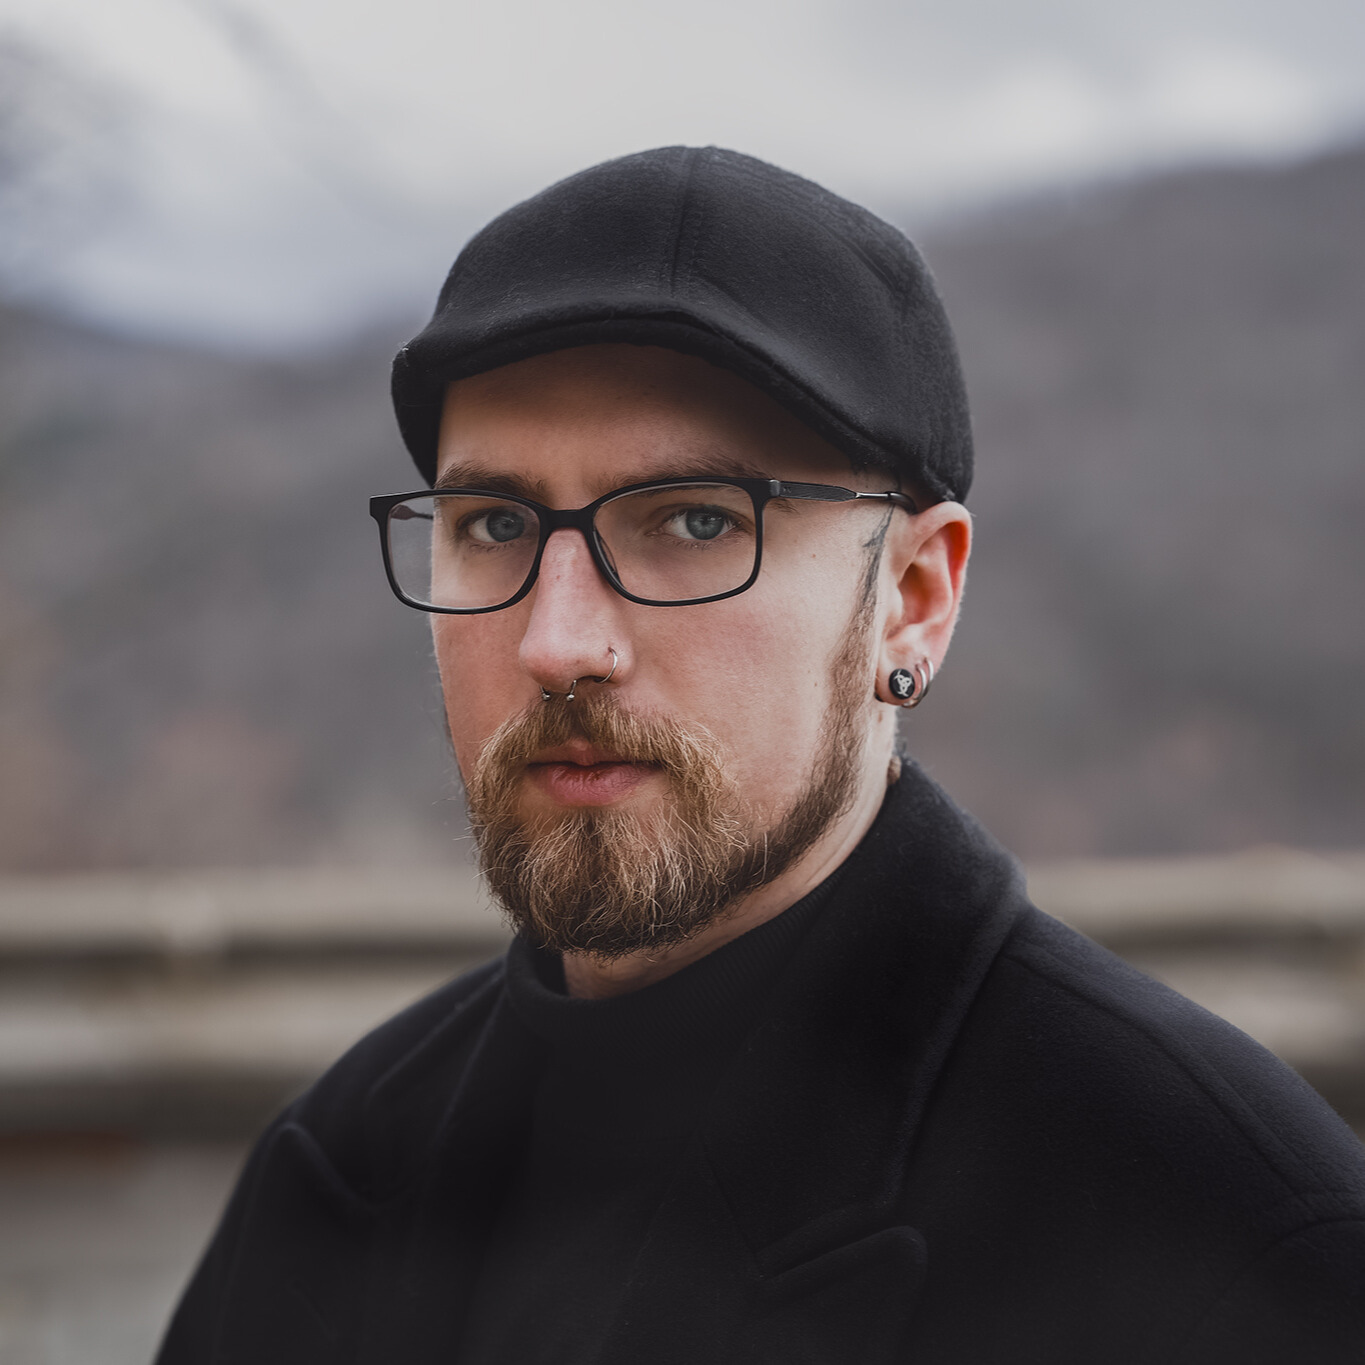
Adrian "Wulf" Weclawski
Offensive Security Consultant
I've worked with web applications for over 8 years — starting on the building side as a full-stack developer, now on the breaking side in offensive security. Every REDWULF engagement is run by me personally, from scoping through to the final report.
Free SaaS Security Checklist
10 critical checks before you launch. No signup required — just your email.
Checklist is on its way!
Check your inbox. I've sent the PDF plus a download link.
No spam. Unsubscribe anytime. Your data stays private.
// Frequently Asked Questions
// Contact
Ready to find out if your product can survive a real attack?
I usually reply within 24h. Initial scope and estimate — no strings attached.
-----BEGIN PGP PUBLIC KEY BLOCK-----

mQINBGoZQysBEADlayEzAlYSmjbr1lHAeo+ZdvJdT7rZtZu3xCCdY5EAZ75RAcLP
X8SK8y3VBeL9p72bZ2R3nZyc58e1gn1+etzssLs6fXQ23HBUPO3lEwn+fNAKXPhO
q/5X29Dnhqx9K6zM7r3TSIEFhpC3ODVFZZT/RAP6FGhCK67XDq+Itw2tl8vzn38s
7aKwLacABd0pDzUfpxI8YdSXH9jWyPDm2cChZlWMdfKqUz9irhNBj0SrqucubBVU
HN97NMAtGlozyUKwGSK7++EVYpwXKlofjm8h9BqBTNdfj0NPb9qFgf9Rj3XPKaCz
bmt95JDKrhksgeB3jvquBPB8oxIIvE0i9CSLa2TFntdTyh/Oq0LaHxDFItbvz4oR
CNrrWezVmskwmX7Eh0rQJ0u12usHhiwLYpU5Ir3ap8fc8zlg5p/z3C62u+31nvuk
TElGyg4av0E0gCcvP0GIVyfpFO9vMfy4cLtgxwHXtkp5feXNqAnO1pu5PZ5YUc/D
dDaTl8YRaeWYWXYYNCQKAX4aAZTeO4YomRdYMDfWfYCJXu00q19J8+z/yXCMMZ7I
/0ogjulcfmWBOxFc8tQsyRpYEzGR5urwviZrwgytn7bft34IE9v0rBVTlSbd0icY
2hdIAFTptng+QAWXGjxPqJb3xYgtZuOPDodK4jRL5eItnWkX8cEeKB11zwARAQAB
tD5BZHJpYW4gV3VsZiAoUkVEV1VMRiBTZWN1cml0eSBDb25zdWx0aW5nKSA8Y29u
dGFjdEByZWR3dWxmLmV1PokCWAQTAQoAQhYhBHzpU2cH94+HHZQ7QRAkoPJy6I18
BQJqGUMrAxsvBAUJA8JnAAULCQgHAgIiAgYVCgkICwIEFgIDAQIeBwIXgAAKCRAQ
JKDycuiNfOycD/9a/DOh6ZC17FIPOXMOoY5zGyArXRRtc96WMAGi0SDWdZ9EPC9v
/oYUOtSBkg237p+/yvNMJ5tlpM4hZeZzjun08BewZpSxuBkR4WG7kU0hDS+HXq1h
Vc7B1Sgtzec/nM3X8GDTvm/j6zJp4DiQrsrvnmEFyKmpzRODufdMy/71Wtdukbqr
TbKUM2PLlbAyAvSYyw1hCvlk509jTIPJdB43Y4DbpMmOV688kuI42ZCps324x5ub
BxKTAXZgzGZdjBCPPuhCn9+sMfworqh7UZ4EVsB5qntYXF4F6WQzFmssWVQtDSxM
VdPaYyde9GtGgkKaNlkCR/8/7+aPCbvlvIETRpT5F6R6BNTZixJnAR8J753rJRaE
1/LgWaNRWz7yc9YLtWFyMPmPKZgsoJVLW7jag5Aeu0h14aa1hX9A2RZaLBrEwtZg
X8lYbpfmxv44GRS148xc8Fexs8ufpZEMV9nNOCHp8MzJWZxxjYIzp/9Spdw6utbM
k0KqfX4GlaLW1JfMgKAG6TlE0/TnRDr3Cw1WwKIefeF1mh/Xbo1JMjBWG5bMRXKN
U5Pnw+7dtm596+HcdkmcUm6m2sDBurbx8mtS6CjoUJIeolIM8kbuE0gpbrKRf4s2
kVEzem2RmDqUHRfV2YpLB7FKzsa23seOE6ZBxo6kvFL+Hil6n9+1v5XZHw==
=YjwI
-----END PGP PUBLIC KEY BLOCK-----
gpg --import on Linux). 3) Encrypt your message with this key before sending. Only the holder of the private key (me) can decrypt it. Use PGP for highly sensitive information or vulnerability disclosures.